
AES vs RSA: Encryption, Differences & Security in 2025
In an era where data breaches and cyber threats are escalating at an alarming rate, encryption has become an essential tool for protecting sensitive information. Whether it's personal data, corporate records, or financial transactions, encryption ensures confidentiality and security. However, despite its critical role, many users and organizations face significant challenges in implementing and managing encryption effectively.
From complex setups and slow performance to difficulties in key management and concerns over quantum computing threats, encryption is not without its hurdles. Moreover, regulatory compliance adds another layer of complexity, making it crucial for businesses to adopt efficient and scalable encryption solutions.
This article delves into the most pressing encryption challenges users face and explores practical solutions to overcome these obstacles, ensuring a secure digital future.

What is AES Encryption?
AES (Advanced Encryption Standard) is a symmetric encryption algorithm adopted by the U.S. government in 2001. It's the gold standard for securing sensitive data worldwide.
Key Features of AES:
- Symmetric encryption: Same key encrypts and decrypts data
- Block cipher: Processes data in 128-bit blocks
- Key sizes: 128, 192, or 256 bits
- Speed: Extremely fast processing
- Security: Mathematically proven secure
How AES Works:
- Input: Original data (plaintext) + encryption key
- Process: Data goes through multiple rounds of substitution and permutation
- Output: Encrypted data (ciphertext)
- Decryption: Same key reverses the process
AES Variants Explained:
- AES-128: 10 rounds, good for most applications
- AES-192: 12 rounds, higher security
- AES-256: 14 rounds, maximum security (government-grade)
Real-World AES Usage:
- File encryption: BitLocker, VeraCrypt
- WiFi security: WPA2/WPA3 protocols
- VPN connections: OpenVPN, IKEv2
- Database encryption: MySQL, PostgreSQL
- Cloud storage: Google Drive, Dropbox
What is RSA Encryption?
RSA (Rivest-Shamir-Adleman) is an asymmetric encryption algorithm invented in 1977. It uses mathematical properties of large prime numbers for security.
Key Features of RSA:
- Asymmetric encryption: Uses public/private key pairs
- Mathematical foundation: Based on prime factorization
- Key sizes: 1024, 2048, 3072, 4096 bits
- Digital signatures: Supports authentication
- Key exchange: Secure key distribution
How RSA Works:
- Key Generation: Create mathematically linked public/private key pair
- Encryption: Use recipient's public key to encrypt data
- Transmission: Send encrypted data safely
- Decryption: Recipient uses private key to decrypt
RSA Key Size Recommendations 2025:
- 1024-bit: Deprecated (vulnerable)
- 2048-bit: Minimum recommended
- 3072-bit: Good for high security
- 4096-bit: Maximum security (slower)
Real-World RSA Usage:
- HTTPS/SSL: Website security certificates
- Email encryption: PGP/GPG systems
- Software signing: Code verification
- SSH connections: Secure remote access
- Cryptocurrency: Bitcoin transactions
AES vs RSA: Detailed Comparison
1. Speed and Performance
AES Speed Advantages:
- Encrypts 1GB file in ~2 seconds
- Hardware acceleration available (AES-NI)
- Minimal CPU overhead
- Perfect for real-time encryption
RSA Speed Limitations:
- Encrypts same 1GB file in ~30+ minutes
- High computational overhead
- No hardware acceleration for large data
- Only suitable for small data blocks
Winner: AES (1000x faster than RSA)
2. Security Strength
AES Security:
- AES-256: 2^256 possible keys (practically unbreakable)
- No known practical attacks
- Approved by NSA for TOP SECRET data
- Quantum resistant with increased key sizes
RSA Security:
- RSA-2048: Secure until ~2030
- RSA-4096: Secure until ~2050
- Vulnerable to quantum computers
- Factorization advances threaten security
Winner: AES-256 (stronger against future threats)
3. Key Management
AES Key Management:
- Same key for both parties
- Secure key distribution challenge
- Key sharing over insecure channels risky
- Simple key storage
RSA Key Management:
- Public key can be shared openly
- No secure channel needed for distribution
- Private key stays with owner
- More complex key infrastructure
Winner: RSA (solves key distribution problem)
4. Use Case Suitability
AES Best For:
- Large file encryption
- Database security
- VPN tunnels
- Disk encryption
- Streaming data protection
RSA Best For:
Certificate-based security
Initial key exchange
Digital signatures
Small message encryption
Authentication systems
Quick Comparison Overview
| Feature | AES | RSA |
|---|---|---|
| Encryption Type | Symmetric (Same key for encrypt/decrypt) | Asymmetric (Public/Private key pair) |
| Speed | Extremely Fast (1000x faster than RSA) | Slow (Complex mathematical operations) |
| Key Sizes | 128, 192, 256 bits | 1024, 2048, 3072, 4096 bits |
| Best Use Case | Bulk data encryption, file storage | Key exchange, digital signatures |
| Security Level | Excellent (AES-256 unbreakable) | Good (RSA-2048+ recommended) |
| Key Distribution | Challenging (same key needed) | Easy (public key can be shared) |
| Quantum Resistance | Vulnerable to quantum attacks | Highly vulnerable to quantum |
| Implementation | Simple and straightforward | Complex mathematical operations |
Difference Between Symmetric and Asymmetric Cryptography
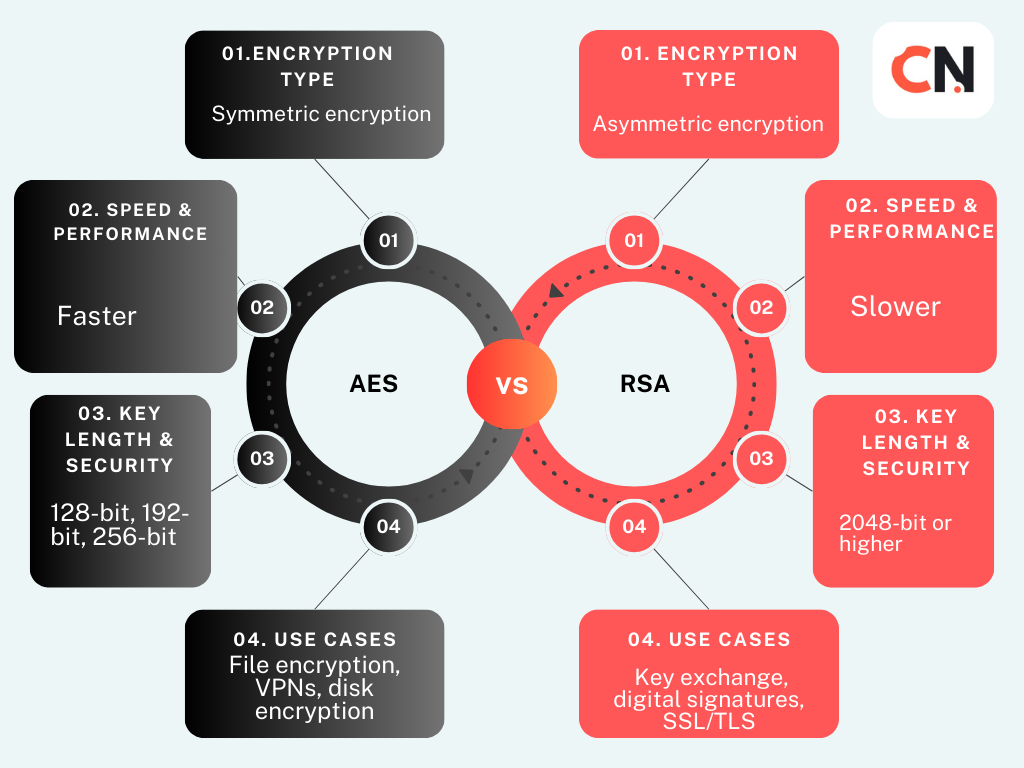
| Feature | Symmetric Encryption | Asymmetric Encryption |
|---|---|---|
| Key Usage | Same key for encryption & decryption | Different keys (public & private) |
| Speed | Faster, efficient for large data | Slower due to complex computations |
| Security | Requires secure key distribution | More secure due to key pair usage |
| Example Algorithms | AES, DES, Blowfish | RSA, ECC, Diffie-Hellman |
| Use Cases | Bulk data encryption, file storage | Secure communication, key exchange |
DES vs AES vs RSA: Three-Way Comparison
| Feature | DES | AES | RSA |
|---|---|---|---|
| Key Size | 56 bits | 128/192/256 bits | 1024-4096 bits |
| Security in 2025 | Broken | Excellent | Good (2048+) |
| Speed | Fast | Very Fast | Slow |
| Encryption Type | Symmetric | Symmetric | Asymmetric |
| Block Size | 64 bits | 128 bits | Variable |
| Quantum Resistance | No | Partial | No |
| Current Usage | None (obsolete) | Widespread | Key exchange only |

Why DES is Obsolete:
- Broken in 1999: Cracked in 22 hours
- 56-bit key: Too small for modern security
- Replaced by AES: Government mandate since 2001
- Never use DES: Security liability
Migration Path:
DES → AES → Post-Quantum Cryptography
AES vs RSA vs ECC: Modern Encryption Battle
Elliptic Curve Cryptography (ECC) Overview:
ECC is a modern asymmetric encryption method offering RSA-level security with smaller key sizes.
| Feature | AES | RSA | ECC |
|---|---|---|---|
| Encryption Type | Symmetric | Asymmetric | Asymmetric |
| Key Size (equivalent security) | 256-bit | 3072-bit | 256-bit |
| Speed | Fastest | Slowest | Medium |
| Mobile Device Friendly | Yes | No | Yes |
| Quantum Resistance | Partial | No | No |
| Adoption Level | Universal | Widespread | Growing |
| Battery Usage | Minimal | High | Low |
ECC Advantages:
- Smaller keys: 256-bit ECC = 3072-bit RSA security
- Faster: 10x faster than equivalent RSA
- Mobile optimized: Lower power consumption
- Future-ready: Better quantum transition path
Current Adoption:
- Bitcoin: Uses ECC (secp256k1)
- iMessage: Apple's preferred method
- TLS 1.3: ECC support required
- IoT devices: Preferred for constrained environments
Which Algorithm Should You Choose?
Decision Matrix:
Choose AES When:
- Encrypting large amounts of data
- Need maximum speed
- Both parties can share key securely
- File/disk encryption required
- VPN or database encryption
Example: Encrypting a 1TB backup drive
Choose RSA When:
- Need secure key exchange
- Parties cannot meet to share keys
- Digital signatures required
- Legacy system compatibility
- Web server certificates
Example: Establishing secure connection to website
Choose ECC When:
- Mobile/IoT applications
- Battery life is critical
- Modern system with ECC support
- Smaller key sizes preferred
- Future-proofing desired
Example: Securing smartphone messaging app
Hybrid Approach (Recommended):
1. Use RSA/ECC for key exchange
2. Use AES for actual data encryption
3. Get benefits of both algorithms
Real-World Implementation Examples
1. Secure Messaging App (WhatsApp/Signal)
Step 1: RSA/ECC key exchange
Step 2: Generate AES session key
Step 3: Encrypt messages with AES
Step 4: Rotate AES keys regularly
2. E-commerce Website Security
Step 1: RSA certificate for HTTPS
Step 2: Browser verifies certificate
Step 3: AES session key negotiated
Step 4: All data encrypted with AES
3. File Encryption Tool
Step 1: User provides password
Step 2: Generate AES key from password
Step 3: Encrypt file with AES-256
Step 4: Store encrypted file securely
4. VPN Connection
Step 1: RSA/ECC authentication
Step 2: Exchange AES tunnel keys
Step 3: All traffic encrypted with AES
Step 4: Periodic key rotation
Code Examples:
AES Encryption (Python):
pythonfrom cryptography.fernet import Fernet

# Generate AES key
key = Fernet.generate_key()
cipher = Fernet(key)

# Encrypt data
plaintext = b"Confidential data"
ciphertext = cipher.encrypt(plaintext)

# Decrypt data
decrypted = cipher.decrypt(ciphertext)
RSA Encryption (Python):
pythonfrom cryptography.hazmat.primitives.asymmetric import rsa
from cryptography.hazmat.primitives import serialization

# Generate RSA key pair
private_key = rsa.generate_private_key(
    public_exponent=65537,
    key_size=2048
)
public_key = private_key.public_key()

# Encrypt with public key
# Decrypt with private key
Security Analysis 2025
Current Threat Landscape:
AES Security Status:
- AES-128: Secure until 2040+
- AES-192: Secure until 2060+
- AES-256: Secure until 2080+
- Quantum threat: Manageable with key doubling
RSA Security Status:
- RSA-1024: Broken (don't use)
- RSA-2048: Secure until 2030
- RSA-3072: Secure until 2040
- RSA-4096: Secure until 2050+
- Quantum threat: Severe vulnerability
ECC Security Status:
- P-256: Secure until 2040
- P-384: Secure until 2060+
- Quantum threat: Similar to RSA
Quantum Computing Impact:
Shor's Algorithm Threat:
- RSA: Completely broken by quantum computers
- ECC: Completely broken by quantum computers
- AES: Reduced security (256-bit becomes 128-bit effective)
Timeline Estimates:
- 2030: Quantum computers threaten RSA-2048
- 2035: Large-scale quantum attacks possible
- 2040: Full quantum threat realization
Performance Benchmarks
Speed Comparison (1GB File):
| Algorithm | Encryption Time | Decryption Time | CPU Usage |
|---|---|---|---|
| AES-128 | 0.8 seconds | 0.8 seconds | 15% |
| AES-256 | 1.2 seconds | 1.2 seconds | 20% |
| RSA-2048 | 45 minutes | 2 minutes | 95% |
| RSA-4096 | 180 minutes | 8 minutes | 98% |
| ECC-256 | 12 minutes | 30 seconds | 60% |
Memory Usage:
| Algorithm | RAM Required | Key Storage |
|---|---|---|
| AES | 16-32 MB | 32 bytes |
| RSA-2048 | 128-256 MB | 294 bytes |
| RSA-4096 | 256-512 MB | 550 bytes |
| ECC-256 | 64-128 MB | 64 bytes |
Hardware Acceleration:
AES Hardware Support:
- Intel AES-NI: 5-10x speed boost
- ARM Crypto Extensions: 3-5x speed boost
- GPU acceleration: 50-100x for bulk data
RSA Hardware Support:
- Limited acceleration: Mainly key generation
- HSM modules: Specialized hardware only
- No consumer GPU support
Best Practices and Recommendations
1. Algorithm Selection Guidelines
For Individual Users:
Personal files: AES-256
Email encryption: RSA-4096 + AES-256
Web browsing: Let browser handle (RSA/ECC + AES)
Messaging: Use apps with hybrid encryption
For Businesses:
Database encryption: AES-256
File servers: AES-256
Web services: ECC-384 + AES-256
Backup systems: AES-256
For Developers:
API security: ECC + AES hybrid
Mobile apps: ECC-256 + AES-256
IoT devices: Lightweight ECC + AES-128
Web applications: TLS 1.3 (handles automatically)
2. Key Management Best Practices
AES Key Management:
- Generate keys randomly: Use cryptographically secure RNG
- Store keys securely: Hardware security modules (HSM)
- Rotate keys regularly: Every 6-12 months
- Backup keys safely: Encrypted offline storage
- Use key derivation: PBKDF2, Argon2, or scrypt
RSA Key Management:
- Minimum 2048-bit keys: 4096-bit for high security
- Protect private keys: Never share or transmit
- Certificate lifecycle: Monitor expiration dates
- Key escrow: For business continuity
- Regular key rotation: Every 2-3 years
3. Implementation Security
Common Mistakes to Avoid:
- Using deprecated algorithms (DES, MD5, SHA-1)
- Hardcoding encryption keys in source code
- Using weak random number generators
- Implementing custom crypto algorithms
- Ignoring padding oracle attacks
Security Checklist:
- Use authenticated encryption (AES-GCM)
- Implement proper padding (OAEP for RSA)
- Validate all inputs
- Use secure random number generation
- Regular security audits and penetration testing
4. Compliance Requirements
Industry Standards:
- FIPS 140-2: U.S. government standard
- Common Criteria: International security evaluation
- ISO 27001: Information security management
- PCI DSS: Payment card industry requirements
Regulatory Compliance:
- GDPR: EU data protection regulation
- HIPAA: Healthcare data protection (U.S.)
- SOX: Financial reporting requirements
- FISMA: Federal information security
Future-Proofing Your Encryption
1. Post-Quantum Cryptography (PQC)
NIST PQC Standards (2024):
- CRYSTALS-Kyber: Key encapsulation mechanism
- CRYSTALS-Dilithium: Digital signatures
- FALCON: Compact digital signatures
- SPHINCS+: Stateless hash-based signatures
Migration Timeline:
2025: Begin PQC evaluation and testing
2026-2027: Pilot implementations
2028-2030: Gradual migration from RSA/ECC
2030+: Full post-quantum deployment
2. Hybrid Classical-Quantum Approach
Transition Strategy:
Phase 1: Current RSA/ECC + AES
Phase 2: Hybrid classical + post-quantum
Phase 3: Pure post-quantum algorithms
Benefits of Hybrid Approach:
- Backward compatibility: Works with existing systems
- Defense in depth: Multiple security layers
- Gradual transition: Reduced implementation risk
- Performance optimization: Balance security and speed
3. Crypto-Agility Implementation
Design Principles:
- Algorithm abstraction: Easy algorithm swapping
- Configuration-driven: Update algorithms without code changes
- Version negotiation: Support multiple algorithm versions
- Monitoring and alerting: Track algorithm usage and vulnerabilities
Implementation Framework:
pythonclass CryptoProvider:
    def __init__(self, config):
        self.symmetric_algo = config.get('symmetric', 'AES-256')
        self.asymmetric_algo = config.get('asymmetric', 'RSA-4096')
        self.hash_algo = config.get('hash', 'SHA-256')

    def encrypt(self, data, key):
        # Use configured algorithm
        pass

    def upgrade_algorithm(self, new_config):
        # Seamlessly upgrade to new algorithms
        pass
Frequently Asked Questions
What's the main difference between AES and RSA?
AES is symmetric encryption (same key for encrypt/decrypt) optimized for speed and bulk data. RSA is asymmetric encryption (public/private key pair) designed for secure key exchange and small data encryption.
Can I use AES and RSA together?
Yes! This is called hybrid encryption. Use RSA to securely exchange an AES key, then use AES to encrypt the actual data. This combines RSA's secure key exchange with AES's speed.
Which is more secure: AES-256 or RSA-4096?
Both are very secure, but they serve different purposes. AES-256 is more future-proof against quantum computing threats. For overall security, use both in a hybrid approach.
Why is RSA so much slower than AES?
RSA uses complex mathematical operations (large prime number calculations) while AES uses simpler bitwise operations. RSA can be 1000x slower for large amounts of data.
How fast is AES encryption in real-world scenarios?
Modern hardware with AES-NI can encrypt at 1-10 GB/second. A typical 1GB file encrypts in 1-2 seconds with AES-256.
Does using longer RSA keys significantly impact performance?
Yes. RSA-4096 is about 8x slower than RSA-2048 for encryption and 4x slower for decryption. The security benefit usually justifies this cost.
Is AES-128 still secure in 2025?
Yes, AES-128 remains secure for most applications. However, AES-256 is recommended for long-term security and regulatory compliance.
When will quantum computers break RSA?
Estimates suggest large-scale quantum computers capable of breaking RSA-2048 may emerge in the 2030s. RSA-4096 might remain secure until the 2040s.
What happens if someone steals my AES key?
If your AES key is compromised, all data encrypted with that key becomes accessible to the attacker. This is why secure key management is crucial.
Should I implement my own encryption algorithm?
Never implement custom encryption algorithms. Use proven, well-tested libraries like OpenSSL, libsodium, or platform-specific crypto APIs.
What's the best key size for RSA in 2025?
Use minimum RSA-2048 for new implementations, RSA-3072 for high-security applications, and RSA-4096 for maximum security. Avoid RSA-1024 (deprecated).
How often should I rotate encryption keys?
Rotate AES keys every 6-12 months or after encrypting ~100GB of data. Rotate RSA keys every 2-3 years or when security standards change.
Which encryption should I use for file backup?
Use AES-256 for file backup encryption. It's fast, secure, and widely supported. Tools like VeraCrypt or BitLocker use AES by default.
What encryption does WhatsApp use?
WhatsApp uses a hybrid approach: ECC (Curve25519) for key exchange and AES-256 for message encryption, implementing the Signal Protocol.
Is it safe to store encrypted data in the cloud?
Yes, if you encrypt data with AES-256 before uploading and keep the encryption key secure (don't store it with the cloud provider).
AES vs RSA: Which should I learn first?
Learn AES first as it's simpler to understand and more commonly used for direct data encryption. Then learn RSA for understanding public-key cryptography concepts.
Is ECC better than RSA?
ECC offers equivalent security to RSA with smaller key sizes and better performance, making it ideal for mobile and IoT applications. However, RSA has broader compatibility.
DES vs AES: Can I still use DES?
Never use DES - it's completely broken and can be cracked in hours. Always use AES for symmetric encryption. Even 3DES is considered deprecated.
How does post-quantum cryptography affect AES and RSA?
Quantum computers threaten RSA severely but only reduce AES security by half (AES-256 becomes equivalent to AES-128). Post-quantum algorithms will replace RSA/ECC.
What's the difference between AES-CBC and AES-GCM?
AES-CBC provides confidentiality only, while AES-GCM provides both confidentiality and authentication. Always prefer AES-GCM for new applications.
Can hardware accelerate both AES and RSA?
Most modern CPUs have AES-NI instructions for hardware-accelerated AES. RSA acceleration is less common and usually requires specialized hardware security modules (HSMs).
My AES encryption is slow. How can I optimize it?
Ensure you're using hardware acceleration (AES-NI), choose an optimized library, use appropriate block cipher modes, and consider parallel processing for large datasets.
I'm getting padding errors with RSA. What's wrong?
Use proper padding schemes like OAEP (RSA-OAEP) instead of PKCS#1 v1.5. Never encrypt data larger than your RSA key size minus padding overhead.
How do I verify my encryption implementation is secure?
Use established crypto libraries, conduct security audits, perform penetration testing, and validate against known test vectors. Never roll your own crypto.
Conclusion: Making the Right Choice
In the battle of AES vs RSA encryption, there's no single winner because they serve different purposes in a comprehensive security strategy. Here's your decision guide:
Quick Decision Framework:
Choose AES When:
- Encrypting large files or databases
- Need maximum speed and efficiency
- Both parties can securely share a key
- Implementing disk or storage encryption
Choose RSA When:
- Need secure key exchange over the internet
- Implementing digital signatures
- Parties cannot meet to share keys securely
- Working with legacy systems requiring RSA
Choose Hybrid (Recommended):
- Building secure communication systems
- Developing web applications
- Need both security and performance
- Want maximum compatibility and security
2025 Security Recommendations:
- Minimum Standards:
- AES-256 for symmetric encryption
- RSA-2048 minimum (RSA-4096 preferred)
- ECC-256 for modern applications
- Future-Proofing:
- Plan post-quantum cryptography migration
- Implement crypto-agility in new systems
- Monitor quantum computing developments
- Best Practice Implementation:
- Use hybrid encryption (RSA/ECC + AES)
- Implement proper key management
- Regular security audits and updates
- Follow industry compliance standards
Final Verdict:
The most secure approach in 2025 is hybrid encryption combining the strengths of both algorithms:
- RSA/ECC for key exchange (solves key distribution)
- AES for data encryption (provides speed and efficiency)
- Post-quantum preparation (future security)
This combination gives you the security of asymmetric encryption with the performance of symmetric encryption, creating a robust security foundation that can adapt to future threats.
Remember: The best encryption algorithm is the one that's properly implemented, regularly updated, and matches your specific security requirements. Stay informed about emerging threats and be prepared to evolve your encryption strategy as technology advances.

Sia is the co-founder of Corenexis and one of the earliest voices shaping its editorial direction. With years of hands-on experience covering AI and technology, she has been writing about the digital world long before it became everyone's favorite topic — and she still does it better than most.
View all posts by Sia →


2 Comments
Can you be more specific about the content of your article? After reading it, I still have some doubts. Hope you can help me.
Can you be more specific about the content of your article? After reading it, I still have some doubts. Hope you can help me.
Community guidelines
We want the comments to be useful for every reader. Every comment is reviewed before it is published. A comment will not be approved if it is:
Keep it genuine and on-topic and it will be approved quickly. Thank you for helping keep the discussion clean.